
Islamabad: Pakistan’s National Cyber Emergency Response Team has warned banks, financial institutions and operators of critical infrastructure to prepare for a new wave of artificial intelligence-driven cyber threats that could disrupt digital banking, payment systems and essential services.
In national cyber advisory NCA 26.051126, the National CERT said cybercriminals could use AI-based tools, automated bots and advanced techniques to find system weaknesses, steal login credentials and launch coordinated attacks at greater speed and scale.
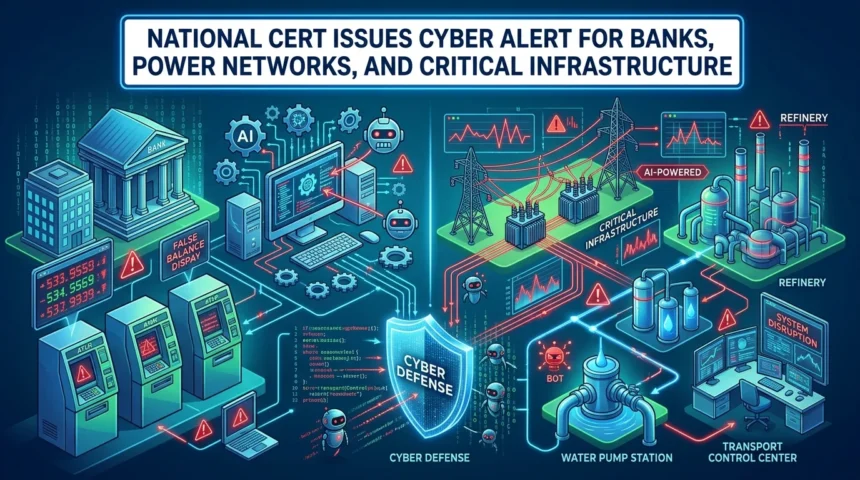
The advisory said one key risk for banks is the manipulation of balances displayed on customer-facing applications. In such a scenario, customers may see incorrect account balances and panic, even if the actual money in their accounts remains unchanged.
According to the advisory, attackers may also target core banking systems, online and mobile banking platforms, application programming interfaces, payment gateways and customer service systems. Such activity could interrupt online services, attempt unauthorised access to customer accounts or breach payment systems.
The nature of the AI threat lies in automation and scale. AI-powered tools can rapidly test large numbers of login credentials, identify vulnerable systems, generate abnormal requests and support coordinated attacks across multiple digital platforms. This could make cyberattacks faster, more complex and harder to detect through routine monitoring.
National CERT urged banks to monitor sudden increases in automated login attempts, repeated password failures, use of stolen credentials, unusual requests through banking applications, unexpected changes in application settings and unusual transaction patterns. It also advised banks to watch for mismatches between core banking records and balances displayed to customers.
Banks have been advised to strengthen the security of core banking systems, digital applications, payment gateways and third-party services. The advisory recommended multi-factor authentication, stronger protection against automated login attempts, strict access controls and regular reconciliation of customer-facing balances with actual banking records.
The warning also covers operational technology systems used in oil and gas facilities, refineries, pipelines, electricity generation and distribution networks, water utilities, manufacturing plants and transport systems.
The advisory said weaknesses in internet-connected devices, industrial control systems and remote access services provided by outside companies could allow attackers to interfere with essential facilities. A successful attack could affect physical operations, including pipeline, refinery and electricity network settings, as well as pressure, temperature, cooling and other industrial controls.
Organisations have been advised to monitor unauthorised access to industrial control systems and SCADA systems, unexpected remote access sessions and suspicious changes in Internet of Things and operational technology devices.
National CERT also referred to recent cyber incidents at European supermarkets involving refrigeration and freezer systems, noting that such incidents showed how attacks on connected operational systems could create physical and business disruption. However, it stated that the use of artificial intelligence in those incidents had not been confirmed.
To reduce risk, organisations have been urged to identify devices and industrial systems directly exposed to the internet, limit direct internet access, especially for remote maintenance connections, and separate office networks from industrial control networks.
The advisory further called for continuous monitoring, timely security updates, backup procedures, improved incident response plans, business continuity arrangements, maintenance of security records and reporting of suspected cyber incidents through relevant national cybersecurity channels.
National CERT, operating under the Government of Pakistan, issued the advisory from the Pak Secretariat in Islamabad. The advisory identifies potential threats and warning signs; it does not report any confirmed cyberattack on a Pakistani bank or critical infrastructure facility.